
Portable SHA-256 block compression, streaming and digest formatting. More...
#include "sha256fst.h"#include <errno.h>#include <fcntl.h>#include <sys/stat.h>#include <unistd.h>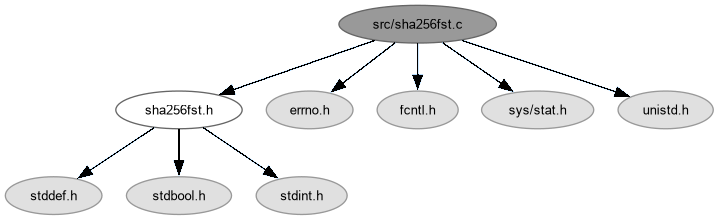
Go to the source code of this file.
Functions | |
| static uint32_t | rotate_right (uint32_t value, unsigned count) |
| Rotate a 32-bit word without signed arithmetic. | |
| static uint32_t | load_big_endian (const uint8_t *bytes) |
| Load a message word safely even when input is unaligned. | |
| static uint32_t | schedule_sigma_zero (uint32_t value) |
| Lowercase sigma-0 for expansion of the message schedule. | |
| static uint32_t | schedule_sigma_one (uint32_t value) |
| Lowercase sigma-1 for expansion of the message schedule. | |
| static uint32_t | round_sigma_zero (uint32_t value) |
| Uppercase Sigma-0 for the first working word in a compression round. | |
| static uint32_t | round_sigma_one (uint32_t value) |
| Uppercase Sigma-1 for the fifth working word in a compression round. | |
| static void | compress_block (struct sha256 *context, const uint8_t *block) |
| Fold exactly one complete input block into the chaining state. | |
| void | sha256_init (struct sha256 *context) |
| Initialize or reset a context for a new message. | |
| void | sha256_append_byte (struct sha256 *context, uint8_t byte) |
| Append one byte to an unfinished message. | |
| void | sha256_append (struct sha256 *context, const void *data, size_t length) |
| Append an arbitrarily aligned chunk; empty chunks are harmless. | |
| void | sha256_finalize (struct sha256 *context) |
| Finish a message, leaving its eight digest words in context->state. | |
| void | sha256_finalize_hex (struct sha256 *context, char *output) |
| Finish a message and write its lowercase hexadecimal digest. | |
| void | sha256_finalize_bytes (struct sha256 *context, void *output) |
| Finish a message and write its standard big-endian digest bytes. | |
| void | sha256_hex (const void *data, size_t length, char *output) |
| Hash one memory region to a lowercase hexadecimal string. | |
| void | sha256_bytes (const void *data, size_t length, void *output) |
| Hash one memory region to its standard 32-byte binary digest. | |
| bool | sha256_file (const char *filename, char output[SHA256_HEX_SIZE]) |
| Hash an immutable nonempty regular file with bounded streaming scratch. | |
Detailed Description
Portable SHA-256 block compression, streaming and digest formatting.
Implements the SHA-256 operations from FIPS 180-4 using unsigned 32-bit arithmetic. Input words and output bytes are explicitly big-endian; neither pointer alignment nor the host byte order affects the result. Complete input blocks bypass the context buffer. The compression schedule occupies a fixed 256-byte local array; no heap or mutable global state is used.
Definition in file sha256fst.c.
Function Documentation
◆ compress_block()
|
static |
Fold exactly one complete input block into the chaining state.
- Parameters
-
[in,out] context Context whose eight chaining words are updated. [in] block Readable SHA256_BLOCK_SIZE-byte region of any alignment.
Does not change the byte count or pending buffer. Working words A-H and the schedule follow the standard directly; uint32_t addition provides the required modulo-2^32 wraparound on both supported architectures.
FIPS 180-4 section 4.2.2 constants, ordered by compression round.
Definition at line 102 of file sha256fst.c.
◆ load_big_endian()
|
inlinestatic |
Load a message word safely even when input is unaligned.
- Parameters
-
bytes Readable four-byte region, most significant byte first.
- Returns
- Decoded word.
Explicit byte loads avoid alignment and strict-aliasing violations. Optimizing compilers can still select native load/byte-reversal instructions.
Definition at line 51 of file sha256fst.c.
◆ rotate_right()
|
inlinestatic |
Rotate a 32-bit word without signed arithmetic.
- Parameters
-
value Word to rotate. count Rotation distance; every caller uses a constant in [1, 31].
- Returns
- Rotated word.
Definition at line 40 of file sha256fst.c.
◆ round_sigma_one()
|
inlinestatic |
Uppercase Sigma-1 for the fifth working word in a compression round.
- Parameters
-
value Current working word E.
- Returns
- XOR of the three SHA-256 rotations.
Definition at line 90 of file sha256fst.c.
◆ round_sigma_zero()
|
inlinestatic |
Uppercase Sigma-0 for the first working word in a compression round.
- Parameters
-
value Current working word A.
- Returns
- XOR of the three SHA-256 rotations.
Definition at line 81 of file sha256fst.c.
◆ schedule_sigma_one()
|
inlinestatic |
Lowercase sigma-1 for expansion of the message schedule.
- Parameters
-
value Earlier schedule word.
- Returns
- Two rotations XORed with a logical right shift.
Definition at line 72 of file sha256fst.c.
◆ schedule_sigma_zero()
|
inlinestatic |
Lowercase sigma-0 for expansion of the message schedule.
- Parameters
-
value Earlier schedule word.
- Returns
- Two rotations XORed with a logical right shift.
Definition at line 63 of file sha256fst.c.
◆ sha256_append()
| void sha256_append | ( | struct sha256 * | context, |
| const void * | data, | ||
| size_t | length ) |
Append an arbitrarily aligned chunk; empty chunks are harmless.
- Parameters
-
[in,out] context Initialized context that has not been finalized. [in] data Readable input of at least length bytes; may be NULL only when length is zero. length Number of bytes to consume.
- Precondition
- The input region must not overlap context storage.
Complete blocks are compressed directly from data. Only partial blocks are copied into the bounded context buffer; no input is retained.
Definition at line 190 of file sha256fst.c.
◆ sha256_append_byte()
| void sha256_append_byte | ( | struct sha256 * | context, |
| uint8_t | byte ) |
Append one byte to an unfinished message.
- Parameters
-
[in,out] context Initialized context that has not been finalized. byte Next input byte.
- Note
- Prefer sha256_append() for chunks to use its direct-block fast path.
Definition at line 181 of file sha256fst.c.
◆ sha256_bytes()
| void sha256_bytes | ( | const void * | data, |
| size_t | length, | ||
| void * | output ) |
Hash one memory region to its standard 32-byte binary digest.
- Parameters
-
[in] data Readable input of at least length bytes; may be NULL only when length is zero. length Input byte count. [out] output Writable SHA256_BYTES_SIZE-byte region, with no trailing NUL.
Uses a temporary stack context; output may overlap the input.
Definition at line 279 of file sha256fst.c.
◆ sha256_file()
| bool sha256_file | ( | const char * | filename, |
| char | output[SHA256_HEX_SIZE] ) |
Hash an immutable nonempty regular file with bounded streaming scratch.
- Parameters
-
filename Input whose size/identity/mtime must remain stable during the read. output Writable SHA256_HEX_SIZE bytes, meaningful only after success.
- Returns
- True after a complete stable read and close, false for I/O or observed mutation.
- Note
- Integrity is not authentication; the producer still owns file/path stability.
Definition at line 286 of file sha256fst.c.
◆ sha256_finalize()
| void sha256_finalize | ( | struct sha256 * | context | ) |
Finish a message, leaving its eight digest words in context->state.
- Parameters
-
[in,out] context Initialized context that has not been finalized.
This consumes the context. Read the final state if needed, then reinitialize; do not append or call another finalizer on the same message. n_bits retains the original input length and buffer_counter becomes zero.
Definition at line 226 of file sha256fst.c.
◆ sha256_finalize_bytes()
| void sha256_finalize_bytes | ( | struct sha256 * | context, |
| void * | output ) |
Finish a message and write its standard big-endian digest bytes.
- Parameters
-
[in,out] context Initialized context that has not been finalized. [out] output Writable SHA256_BYTES_SIZE-byte region, with no trailing NUL.
- Precondition
- Output must not overlap context storage.
- Note
- This consumes the context, just like sha256_finalize().
Definition at line 262 of file sha256fst.c.
◆ sha256_finalize_hex()
| void sha256_finalize_hex | ( | struct sha256 * | context, |
| char * | output ) |
Finish a message and write its lowercase hexadecimal digest.
- Parameters
-
[in,out] context Initialized context that has not been finalized. [out] output Writable SHA256_HEX_SIZE-byte region, including the trailing NUL.
- Precondition
- Output must not overlap context storage.
- Note
- This consumes the context, just like sha256_finalize().
Definition at line 249 of file sha256fst.c.
◆ sha256_hex()
| void sha256_hex | ( | const void * | data, |
| size_t | length, | ||
| char * | output ) |
Hash one memory region to a lowercase hexadecimal string.
- Parameters
-
[in] data Readable input of at least length bytes; may be NULL only when length is zero. length Input byte count. [out] output Writable SHA256_HEX_SIZE-byte region, including the trailing NUL.
Uses a temporary stack context. Output may overlap the input because all input is consumed before the digest is written.
Definition at line 272 of file sha256fst.c.
◆ sha256_init()
| void sha256_init | ( | struct sha256 * | context | ) |
Initialize or reset a context for a new message.
- Parameters
-
[out] context Writable caller-owned context.
- Note
- Initialization is not a secure erasure of previous buffer contents.
Definition at line 168 of file sha256fst.c.